Last week, the cryptocurrency ecosystem was rocked by a major security breach when suspected North Korean hackers successfully exploited the crypto exchange Bitget, making off with an astounding $387.5 million in digital assets. In the immediate aftermath of the exploit, blockchain investigators swung into action, quickly flagging the attacker’s recipient addresses and tracing the flow of the stolen funds across public networks. What followed, however, has ignited a fierce industry-wide debate over the responsibilities, vulnerabilities, and legal realities of decentralized finance (DeFi).
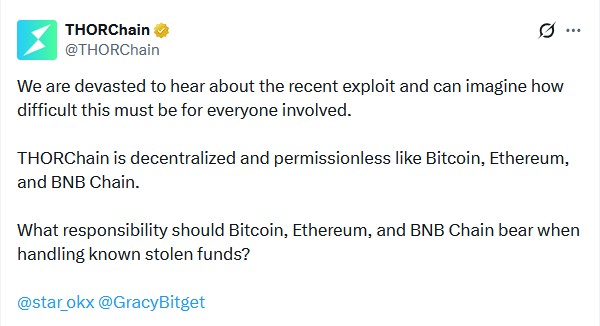
Bitget CEO Gracy Chen stepped into the controversy by publicly demanding that decentralized cross-chain swaps platform THORChain "refuse service to these addresses." The demand placed a spotlight on the friction points between centralized exchange security requirements and the core ethos of permissionless, immutable protocols.
THORChain did not mince words in its refusal, responding publicly with a pointed comparison: "THORChain is decentralized and permissionless like Bitcoin, Ethereum, and BNB Chain. What responsibility should Bitcoin, Ethereum, and BNB Chain bear when handling known stolen funds?"
The standoff quickly drew intense scrutiny across the crypto community. The controversy is particularly sharp given THORChain’s own history; the protocol was forced to halt operations immediately in May following a separate $10.7 million exploit of its own funds. Complicating matters further, THORChain permanently retired its admin key in February 2025, meaning the protocol no longer possesses an easy, centralized mechanism to censor or block specific addresses even if its developers or community wished to do so.
This is not the first time THORChain has found itself at the center of such a storm. The protocol was previously utilized to swap roughly $1.2 billion of the funds stolen during the massive $1.46 billion hack of Bybit—an incident that coincidentally unfolded just 11 days after THORChain had retired its admin key.
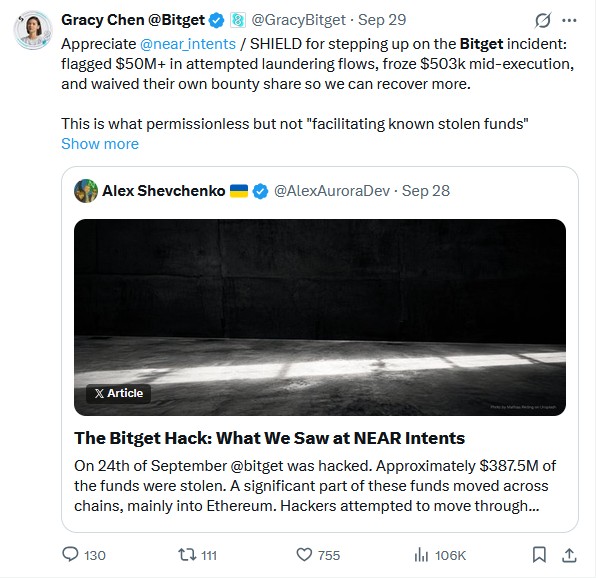
In stark contrast to THORChain’s hands-off stance, NEAR Intents adopted the exact opposite approach. Utilizing its automated SHIELD program, NEAR Intents successfully blocked addresses linked to the Bitget hack from swapping $50 million on its platform. In a demonstration of its commitment to blocking illicit funds, NEAR Intents even turned down the 5% bounty offered by Bitget for intercepting the transactions.
While praised by centralized entities like Bitget, NEAR Intents’ intervention has drawn sharp criticism from "decentralization maximalists," who argue that programmatic interference undermines the core tenet of permissionless finance.
To unpack the complex legal landscape governing these diverging philosophies, Cointelegraph’s Magazine sat down with Yuriy Brisov from D&A Partners to discuss the liabilities, risks, and regulatory precedents shaping the modern DeFi space. Below is an edited version of that conversation.
Magazine: Bitget asked THORChain to block funds tied to the hack, and it responded saying it’s decentralized and permissionless. Is that a legal defense? Do they have an obligation to block those addresses?
Brisov: It depends on the level of decentralization. So when they do this — when they block some addresses — they show that their nodes aren’t truly decentralized. It’s good for the community, when they can use this power to prevent some malicious activities. However, at the same time, they open themselves to any other legal claim. Their only protection is “we are decentralized.”
In the Uniswap case, they said ‘we are truly decentralized and there is nothing we can do.’ [Investors sued Uniswap after buying 38 rugpull and scam tokens, but a judge dismissed the case in March — Ed.]
And this is the strongest defense for any DeFi protocol. If they show that they can block, control, or somehow interfere — even in a good faith attempt to prevent fraud — they still open themselves for these kinds of claims. That if you have control, then maybe your control shouldn’t be limited to only obvious fraud cases. You should imply [control over] due diligence matters. You should apply KYC and AML protective measures.
Magazine: NEAR Intents blocked those addresses, and Bitget thanked them for doing so. Does that mean NEAR has shown Intents is not decentralized and will therefore need to interfere in lots of other situations?
Brisov: If you show that you have control over assets, then you potentially open yourself to all potential claims regarding pump-and-dump schemes, volatility, or any other potential claims of any investors who somehow have been damaged and harmed. And they can now say that you have control. Why do you use it in one case and not use it in another case? Why don’t you check all your token issuers on your platform? Why don’t they provide KYC forms like on any centralized exchange?
Magazine: THORChain argues the protocol halt in May initially triggered by an automated system and that they don’t have the ability to block certain addresses. If true, is that a defense?
Brisov: It might be. We don’t know yet, because it hasn’t been challenged yet. But any amount of control makes any DeFi project weaker vis-à-vis any claimant.
Magazine: On the other hand, the protocol could upgrade the software if it wished to block certain addresses. Could a project get in legal trouble for being reckless or negligent if they don’t impose something like that?
Brisov: It depends on how it’s been done from the technical side. Say there is an oracle that can detect any North Korean IP and block it automatically, and there is no person who sits and presses a button — “there’s a North Korean hacker, let’s block him.” Then it’s okay.
If there is a team that oversees the situation and says, “Okay, we can see this is an illicit activity, we block these addresses, we press the button manually.” From the legal point of view, even though it’s a good act and it benefits the community, it still makes the project not fully decentralized from the legal perspective, and it strips you of the protection that regulations like MiCA [EU’s Markets in Crypto Assets laws] or the general understanding the SEC and CFTC provide that if you’re fully decentralized, you cannot be liable for the actions of the participants in your ecosystem.
Magazine: NEAR’s technology is called SHIELD and it’s an automated process that identifies addresses associated with known hacks on public blockchains and then blocks them from accessing Intents automatically. Does that mean it’s more likely to be seen as decentralized?
Brisov: Definitely. They show that they are good-faith actors trying to [add] protective measures into their protocols. There is no compliance team, people who sit there and control the operation manually. This is a smart solution, and that’s what we recommend to all the DeFi companies.
Magazine: In February 2025, THORChain retired the admin key which would allow them to make those sorts of unilateral changes. With the lack of an admin key and the fact they’ve got a hundred validators, does that make them sufficiently decentralized?
Brisov: More likely than not, but we can’t say that for sure. I would say yes.
Magazine: THORChain is not a mixer. You can take stolen Bitget funds and swap them on THORChain, but when it comes out the other end, it will still be transparently linked to the Bitget hackers. How does that fit the definition of money laundering? Or is it receiving stolen goods?
Brisov: I don’t see how they can be liable for money laundering because even Tornado Cash, that was, to a certain extent, made to launder money [avoided US sanctions as immutable smart contracts are not sanctionable property in terms of money laundering — Ed].
American law treats something as either property or not property. And money laundering is illegally moving property through the legal channels. You make proceeds of illicit activity, and it’s property, and then you move it through some channels and try to make it legal. But smart contracts are not property at all. You don’t control them. You don’t own them. That’s how Tornado Cash won their case in court vis-à-vis OFAC sanctions. They just proved that they don’t have any control over their smart contracts.
Magazine: The Bybit hack happened 18 months ago. Does that mean that no legal action is going to be taken against THORChain, or do these cases just take a long time?
Brisov: It might happen in the future, definitely. After the Bybit case, they seriously opened themselves for potential claims.